Posted on September 17, 2026
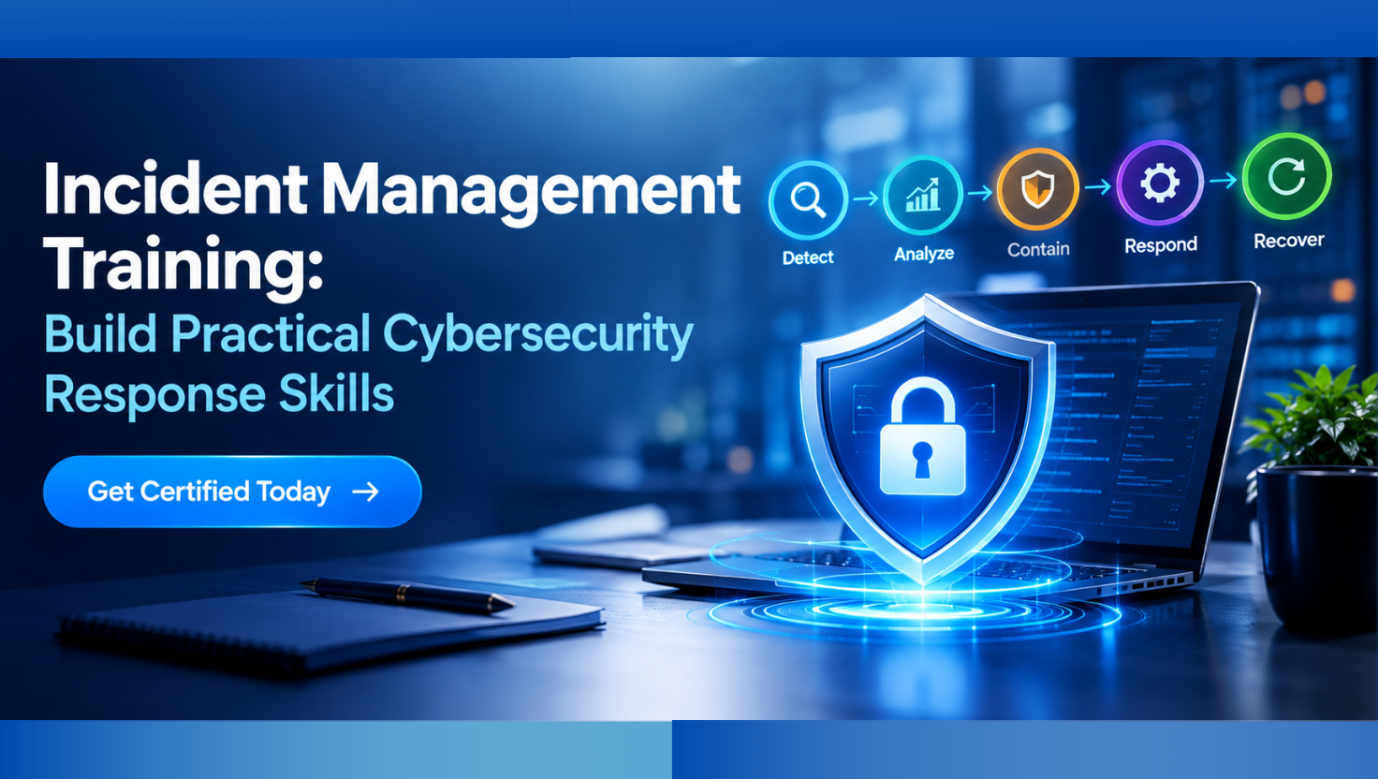
Cybersecurity attacks might affect business processes negatively, expose sensitive data, and create significant difficulties during recovery. In light of the increasing complexity of cybersecurity threats, professionals require systematic knowledge and practical skills to deal with such incidents effectively. Incident management training enables professionals to develop the skills needed to identify, analyze, contain, and respond to […]

Posted on August 6, 2026
With the arrival of the NIS2 Directive, the cybersecurity landscape in Europe is experiencing an enormous change. All organizations that will operate in sectors of high importance would have to upgrade their governance, be cyber resilient, and adhere to strict security regulations. As a cybersecurity professional, compliance manager, IT professional, consultant, or auditor, it is […]

Posted on July 8, 2026
In view of the growing number of cyber-attacks and strict regulatory compliance requirements, individuals who possess knowledge and skills in information security are highly sought after today. Taking the self-paced ISO 27001 courses is therefore a great idea that will help you enhance your auditing and compliance skills while keeping your schedule flexible. As an […]

Posted on July 8, 2026
There are several reasons why the cybersecurity industry is one of the best industries. Such include the growth in cyber threats, compliance issues, and the overall digital transformation witnessed in different sectors. Organizations including financial service providers, healthcare facilities, the government, and technology companies require cybersecurity experts. While cybersecurity courses continue to be popular, many […]
Posted on June 19, 2026
Regulations pertaining to cybersecurity have become quite essential today due to several reasons such as the emergence of new threats to cybersecurity, the increased compliance requirements as well as accountability in the field. The NIS2 Directive from the European Union is an important development that would increase cybersecurity resilience in important and critical sectors. The […]